

**Book a free security consult →
Most breaches I investigate start with a door, not a firewall. You secure a company in 2026 by uniting physical, cyber, personnel, information, and operations under one risk-led plan, with clear owners and budgets. This complete guide corporate security shows you how to design that plan, stage by stage, without waste.
Here’s the plan in one line: map what you must protect, model what can hurt it, build layered controls, then monitor and drill until response is muscle memory. That’s not theory. It’s what reduces loss events, improves insurance posture, and keeps audits calm.
However, tight budgets and mixed tech stacks make this hard. For example, guards and cameras help little if alerts lag or logs never get read. Therefore, we’ll focus on low-friction moves you can make this week and the deeper moves you can phase in this quarter. And yes, we’ll keep 2026 realities in mind: hybrid work, AI-enhanced video, and sharper privacy rules.
What Corporate Security Actually Covers (And Why Most Companies Get It Wrong)
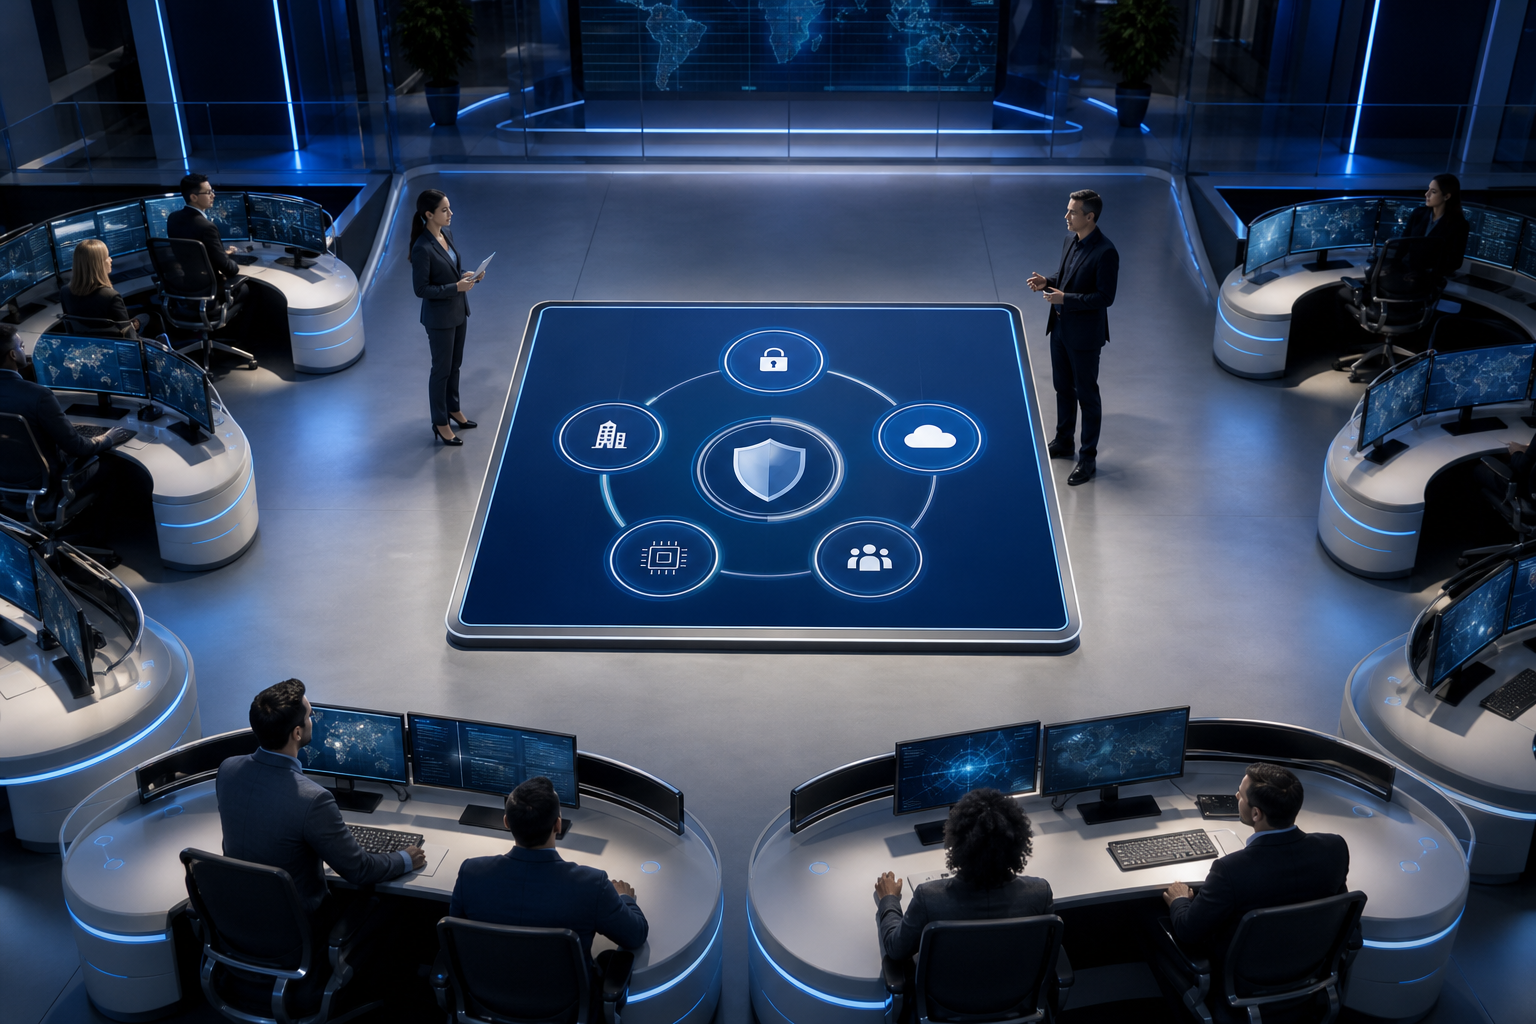
Corporate security is not just badges and malware scans. It is the union of five domains that affect daily operations and brand trust. For example, an access badge disabled in HR records but still valid at the server room door is more than a glitch. It’s a gap an attacker can walk through.
When these live in silos, risk hides in the seams.
According to VideoraIQ deployment data, 85% of CCTV footage is never reviewed. That’s sunk cost without risk reduction. The issue isn’t cameras; it’s the workflow. If you can’t search, flag, and act in real time, storage becomes a passive archive rather than a live sensor grid.
When physical and cyber collide
Moreover, cyber and physical risks now feed each other. A propped dock door can lead to a stolen workstation. A phished VPN account can disable alarms before a theft. Therefore, you need shared playbooks, common language, and linked alerts across teams.
In this complete guide corporate security, think “one plan, many layers.” Budget owners differ by layer, but risks don’t respect org charts. So you align incentives, metrics, and drills so each domain boosts the others.
The five domains at a glance
- Physical: doors, cameras, guards, barriers, visitor flows.
- Cyber: identity, endpoints, networks, apps, SaaS, data.
- Personnel: background checks, insider risk, training, culture.
- Information: data classification, retention, privacy by design.
- Operational: supply chain, facilities, business continuity, safety.
“Silos don’t fail loudly. They fail quietly, at 2 AM, when two teams think the other one is watching.”
How to Build a Corporate Security Program: A 7-Step Framework
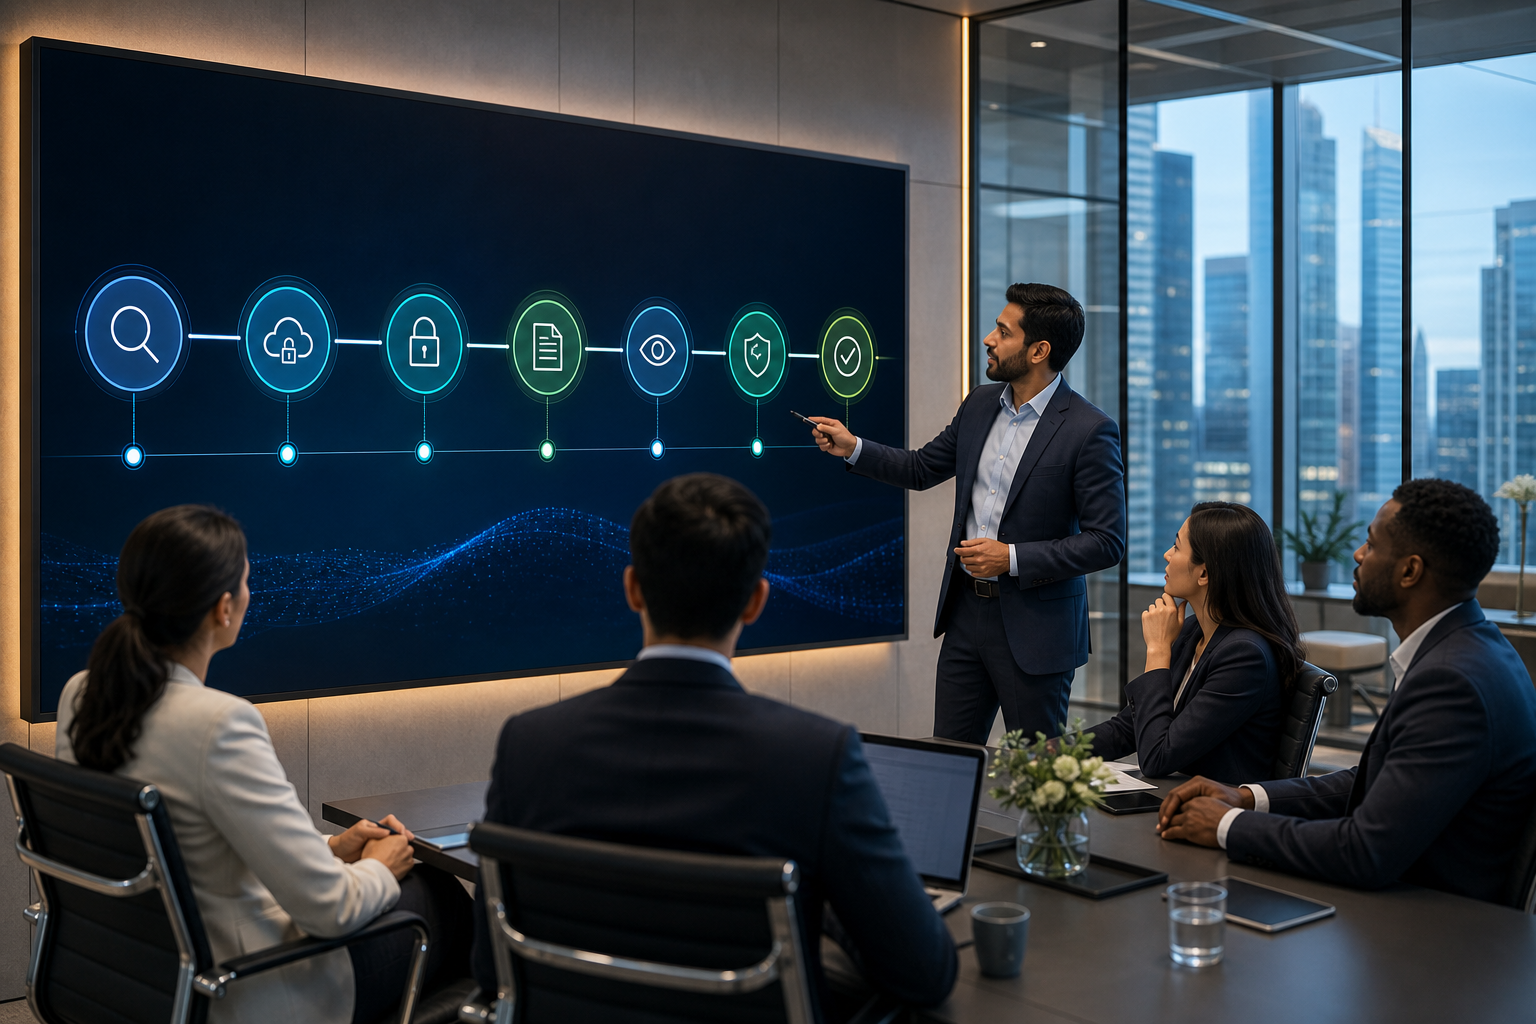
You don’t need a blank check to raise your posture fast. You need sequence, clear owners, and checks that trigger action. Use the steps below to build a program that stands up in audits and stands firm in real incidents.
First, set direction. Tie security goals to top risks and to revenue operations. Then, phase changes by impact and complexity. As a result, you move fast without breaking trust or workflows in 2026’s hybrid work reality.
-
Risk assessment: Identify top loss scenarios by likelihood and impact. Use the NIST Cybersecurity Framework as a simple map for identify-protect-detect-respond-recover.
-
Asset inventory: List sites, cameras, doors, servers, SaaS apps, and crown-jewel data. Tag owners. Without owners, nothing gets fixed.
-
Threat modeling: Map how threats reach assets. Include insider misuse, tailgating, lost devices, and cloud misconfigurations. Keep it narrative and short.
-
Layered controls: Pair physical and digital. Use access control plus MFA. Add camera “zone-based monitoring” to high-risk areas. Gate admin tools to secure networks.
-
Monitoring & alerting: Send “real-time alerts with video proof, location tag, and timestamp.” Route to on-call, not inboxes. Measure mean time to acknowledge.
-
Incident response plans: Build short, printable runbooks. Assign roles, comms templates, and legal/PR contacts. Run drills each quarter.
-
Regular audits: Check doors, logs, and alerts. Use “heatmaps and analytics for security planning” to find dead zones and peak risk hours.
Putting it together: a quick example
- A warehouse maps dock, yard, and cashier zones as high risk. They enable zone-based monitoring on those cameras and set alerts to on-call radios.
- They test a theft scenario: a box moved past a “line-cross” rule at 22:00. The alert links the clip and camera location. The supervisor responds in under 90 seconds. Next, they tighten access after-hours and log reviews weekly.
As a result, you now have a live feedback loop. Each alert teaches you where to add light, change a rule, or update training. Use this complete guide corporate security framework to keep that loop tight and simple.
**Get a free 20‑min review today →
Also Read!
How to Add AI to Existing Security Cameras for Corporate Offices and Campuses
Best Fire Smoke Detection Security Camera for Corporate Offices and Campuses in 2026
5 Common Corporate Security Mistakes That Create Gaps
Security fails more from small misses than master hackers. Fixing these five mistakes will cut risk fast and save budget.
1) Over-relying on guards without tech support
Guards help, but they blink, get pulled to other tasks, and cover large areas. Pair fewer guards with smarter sensors. For example, add line-cross rules at exits and door-forced alerts back to radios. Therefore, every guard hour defends more ground.
2) Installing cameras but never reviewing footage
Storage without action is a sunk cost. Instead, shift to live alerts, smart search, and daily exception reviews. For example, pull a 10-minute “events only” reel each morning for your top three risk zones. Then fix what the reel shows.
3) Ignoring insider threats
Most programs track outsiders well and insiders poorly. Build for misuse, not malice. For example, alert on after-hours access to cashier or finance zones and match badge logs to camera clips. As a result, you deter and detect quiet loss.
4) No protocol for unattended objects
Unattended bags or tools can mean safety risks or theft staging. Use “customizable time thresholds for detecting unattended items” so alerts match your environment. In a lobby, 2 minutes. In a staff area, 10. Then test and tune monthly.
5) Treating compliance as the ceiling
Compliance is the floor. It keeps fines away. It doesn’t stop theft or fraud. Start with controls that block real threats, then map them to standards. You’ll pass audits and cut loss at the same time.
As part of the complete guide corporate security, bake these fixes into your first quarter plan. Small changes here yield fast, visible wins your exec team will back.
Tools and Technologies Shaping Corporate Security Today
Tools should fit your risks, not the other way around. The right stack connects doors, cameras, identities, and events into one timeline you can act on. However, keep privacy and legal review in the loop. Link your controls to data retention and user consent standards like the GDPR.
- Access control systems: Badge, mobile credentials, role rules, visitor flows.
- AI video analytics: Object, line-cross, intrusion, face recognition where legal.
- SIEM/XDR platforms: Unified logs and detections across cloud, endpoints, and identity.
- Visitor management: Pre-registration, watchlists with policy guardrails, badge print.
- Threat intelligence: Feeds mapped to your assets, not generic noise.
Tools like VideoraIQ (AI video analytics) are worth shortlisting as one option among several categories. Its platform offers 9 AI detection engines, “real-time alerts with video proof, location tag, and timestamp,” zone-based monitoring, and heatmaps for planning. It works with existing cameras across 200+ brands, is cloud-based with no need for on-premise servers, and is GDPR compliant and HIPAA compliant. For a neutral control map, pair analytics with your SIEM and access control so cyber and physical alerts land on the same incident card.
Moreover, align tool choices to recognized frameworks. For example, map controls to the GDPR (Regulation (EU) 2016/679) principles of data minimization and storage limits. Therefore, privacy reviews speed up and audits stress less.
Finally, plan for 2026 growth. Choose tools that scale across sites and teams without forklift upgrades. If you add five sites next year, your license, storage, and alerting should scale with a few clicks, not a forklift.
What to Do This Week: Your Corporate Security Quick-Start Checklist
You don’t need a six-month project to get moving. Do these now. Each task takes under an hour and pays back fast.
-
Audit camera coverage: Print a floor map and mark dead zones in red.
-
Test alert response: Trigger a safe test. Time alert-to-ack and alert-to-arrival.
-
Review access logs: Pull last 30 days. Flag after-hours and weekend entries.
-
Identify unmonitored zones: Label high-value areas without cameras or sensors.
-
Tabletop exercise: Run a 20-minute theft scenario with duty leads.
-
Set unattended-object thresholds: Pick times by zone, then test one alert.
-
Create a one-page IR card: Roles, contacts, and first three actions.
As you run this checklist, capture gaps and quick wins. Then plug them into your next two sprints. Use this complete guide corporate security as your running plan, not a one-time read.
**Book a zero-cost gap review →
Key Takeaways
- Unite physical, cyber, personnel, information, and ops under one risk-led plan.
- Convert cameras from storage to sensors with real-time, actionable alerts.
- Build the 7-step program, then drill and audit to keep it sharp in 2026.
- Fix five common gaps now: guard-overreliance, unreviewed video, insider risk, no object protocol, compliance-only mindset.
- Choose tools that work with your stack, protect privacy, and scale across sites.
You’re closer than it seems. Start with the quick wins, wire alerts to people who can act, and keep tuning. By next month, you’ll see faster responses and fewer losses.

