

Buying facial recognition on “accuracy” alone is a mistake. If you need to choose facial recognition system in 2026, start with your use case, verify independent results, and pilot on your own video before you sign anything. Here’s the short path: define the job, check independent NIST results, assess bias, confirm privacy, integrate with your stack, and run a pilot.
You care about speed, false alarms, and how it copes with glare, masks, hats, and crowds. You also care about privacy rules and consent. That mix, not a glossy demo, is what separates a smart pick from a costly one.
For context, VideoraIQ reports that 85% of CCTV footage is never reviewed. You probably feel this too: too many cameras, not enough eyes. That’s why real-time alerts, tested thresholds, and clean integrations matter. This guide gives you a practical, vendor‑neutral way to make a call you can defend, in a budget review, a board meeting, or a courtroom.
Moreover, you’ll see how to weigh 1:1 checks (Are you the person you claim to be?) against 1: N searches (Who is this person from a gallery?). In addition, you’ll get a simple test plan you can run in one week. By the end, you will be able to choose with confidence and explain your choice clearly.
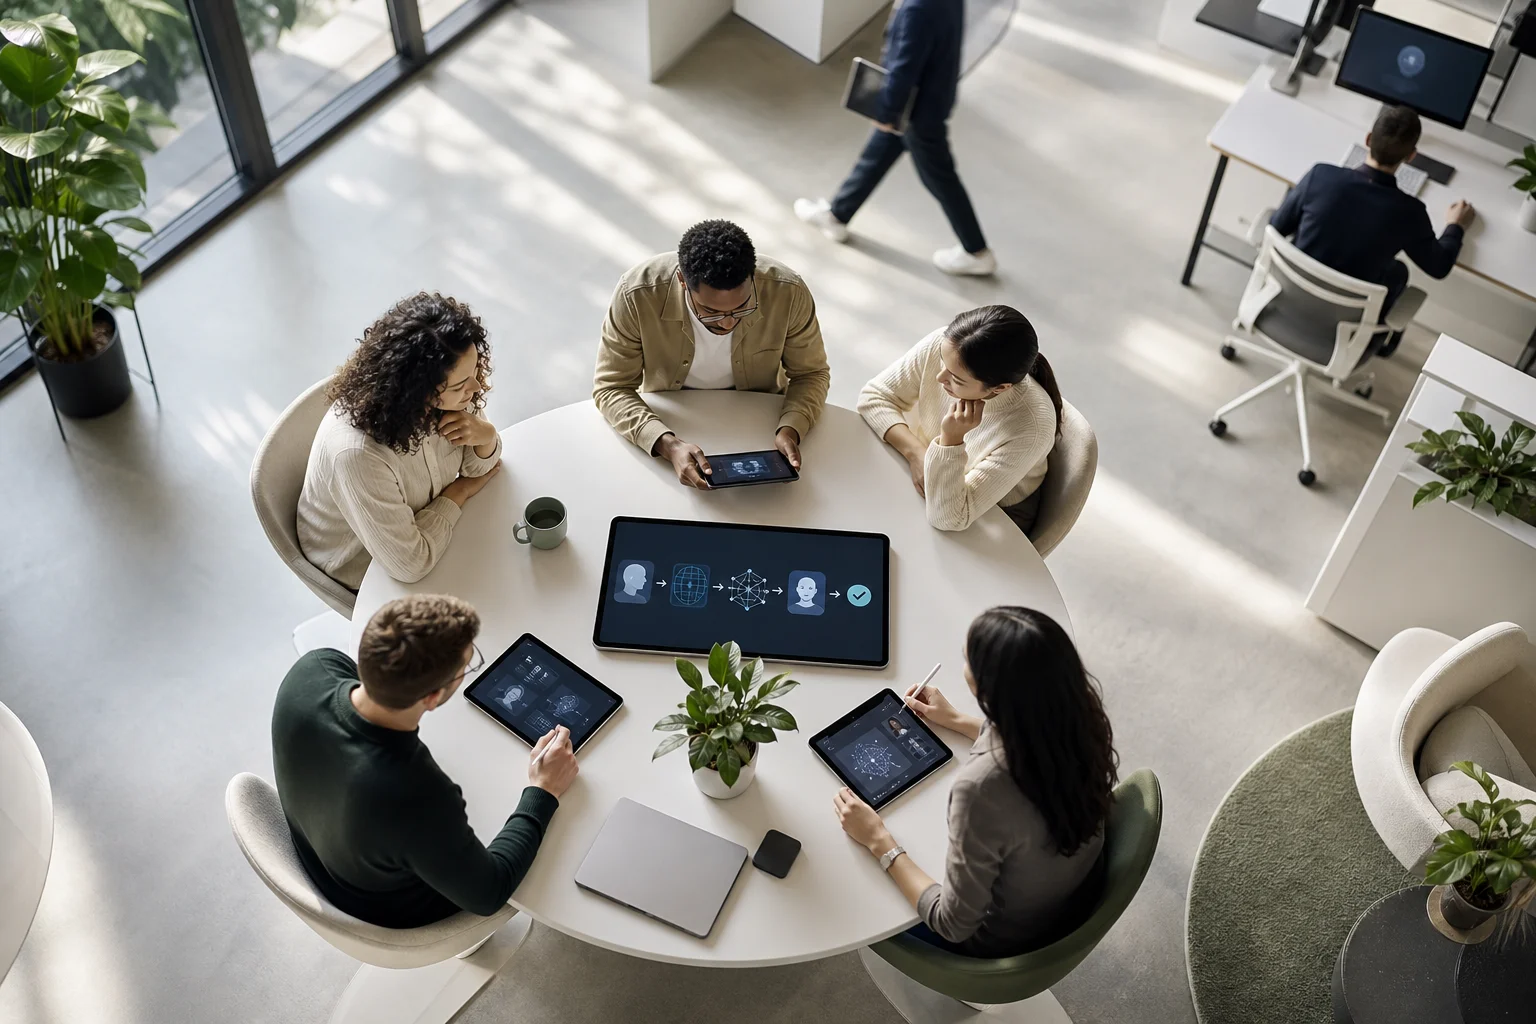
What Is a Facial Recognition System and How Does It Actually Work?
At a high level, a face system turns pixels into numbers, then compares those numbers fast. The magic is in how it cleans the image and how it measures “closeness.” But the pipeline is simple once you see it.
- Detection: Find faces in the frame.
- Alignment: Rotate and crop so eyes, nose, and mouth line up.
- Feature extraction: Convert the face into a compact vector (a “faceprint”).
- Matching: Compare that vector to one or more stored vectors and score the match.
Each stage matters. For example, poor detection or bad alignment can sink accuracy before matching even starts. Sharp, well-lit footage helps, but a good system must still work on grainy cameras and odd angles.
Modes: 1:1 vs 1: N
There are two main modes. In 1:1 verification, the system checks if a live face matches a specific enrolled face. Think secure door unlocks or time-and-attendance. In 1: N identification, it tries to find the person in a gallery of faces.
Think watchlists or finding a VIP guest at a stadium. As a rule, 1:1 is faster and more accurate because the search space is tiny. 1: N scales harder and needs tighter controls to avoid false alerts.
Platform context and claims
Furthermore, face recognition is often one engine within a larger video AI stack. Some platforms ship with 9 AI detection engines including face recognition, intrusion detection, fire and smoke, and more. That bundle can reduce vendor sprawl and help you connect alerts, such as linking a face alert to a boundary breach in the same zone.
Accuracy claims vary, and context is everything. A vendor might cite “99.4% detection accuracy” for certain scenarios. Treat any single figure as a clue, not a verdict. Ask for details: camera resolution, lighting, occlusions, and whether the test was 1:1 or 1: N.
Plain-English Example
- Verification (1:1): “Is this Amira at the door?” The system compares one live face to Amira’s stored face. Quick yes/no.
- Identification (1: N): “Who is this person in the lobby?” The system searches the face across a gallery (dozens to millions). It returns the best matches with scores.
Also Read!
How to Evaluate a Facial Recognition System: A Step-by-Step Framework
You can pick a strong platform in days, not months, if you structure the test. The sequence below keeps you honest and keeps vendors focused.
First, set the bar in writing. Then, test on your own footage. Finally, check privacy and security so you can pass audit and legal review.
Define scope and risk
-
Define your use case and risk.
Be specific. “Find banned entrants at Gate B within three seconds” beats “Improve security.” Note lighting, camera angles, masks, peak crowd size, and failure costs. Decide if you need 1:1, 1: N, or both. -
Check independent accuracy benchmarks (NIST FRVT).
Review the latest NIST Face Recognition Vendor Test (FRVT) for verification and identification tracks. Look for ranking stability over years, not one lucky run. Match your use case to the right NIST test type.
Check accuracy and fairness
-
Assess bias and demographic fairness.
Demand per‑group metrics (age bands, skin tones, and genders) from the vendor’s audits. Ask how they reduce bias in training and thresholds. For public deployments, document your fairness review and who signs off. -
Verify privacy and legal compliance. Map data flows: capture, transmit, store, and delete. Confirm encryption, audit logs, and role-based access.
In the EU, align with GDPR principles (lawful basis, purpose limits, retention). You can read GDPR text at eur-lex (GDPR). In healthcare sites, ask for HIPAA compliant handling of any footage that may include PHI.
Integration and performance
-
Test integration with your stack.
Confirm it works with existing cameras across 200+ brands, supports RTSP/ONVIF, and sends alerts to your VMS, SIEM, or messaging tools. Measure alert delay; sub-3 seconds (<3 seconds alert latency) is realistic for live response. Avoid custom hardware unless you truly need on‑prem. -
Run a pilot with real footage. Use one high-traffic zone and one hard zone (glare, hats, or backlit entries). Enroll 50–200 consented faces.
Log false accepts and false rejects per day. Track operator workload and time-to-respond. Keep the pilot to 30 days, then decide.
Instrumentation and auditability
Moreover, insist on exportable logs: match scores, thresholds, operator actions, and timestamps. Those records will help you tune thresholds and defend decisions if you face a complaint.
Practical tip: Write your pass/fail gates before you start vendor demos. Vendors can’t move the goalposts if you nail them to the ground.
To keep the process lean, set a threshold for “good enough.” For example, “1: N watchlist match within 3 seconds, with fewer than two false alerts per camera per day.” Then hold every vendor to that same bar.
Finally, include security assurances in your scorecard. Look for proof of GDPR compliant and HIPAA compliant claims, documented encryption at rest/in transit, and admin controls for least‑privilege access.
5 Common Mistakes When Selecting Facial Recognition Technology
Teams rarely fail from lack of features. They fail from process gaps that skew the choice. Here are the traps I see most in real projects.
-
Ignoring lighting and angles.
Harsh backlight, caps, and half profiles can tank match rates. Test noon glare, night shadows, and human behaviors like head turns. -
Skipping demographic bias testing.
If you don’t request per‑group metrics, you won’t know where it fails. Push vendors for numbers across skin tones, ages, and genders. Make someone own this review. -
Overlooking privacy impact assessments.
Without a DPIA or risk review, legal blockers show up late. Map what you store, who can see it, and how long you keep it. Set deletion rules up front. -
Choosing on‑prem when cloud fits better.
On‑prem can add hardware, patching, and delays. If you have elastic peaks or many sites, cloud can cut time-to-deploy. A cloud-based approach with no need for on-premise servers is common in 2026. -
Not testing with real-world footage.
A lab demo proves little. Pilot on your cameras with your crowd and your lighting. Measure results daily and adjust thresholds.
In addition, look for platforms that report a low false alarm rate through pattern recognition. That matters because alert fatigue kills trust. VideoraIQ reports that 85% of CCTV footage is never reviewed; real-time face alerts can turn that idle video into action the moment it counts.
Therefore, write down success metrics for your pilot: time to alert, operator load, false alerts per camera, and match quality in hard scenes. Then decide with data, not hope.
Include the phrase “choose facial recognition system” in your pilot doc as your decision driver, so your team frames the test around outcomes, not features.
Also Read!
How to Choose Face Recognition and License Plate Camera Software for Corporate Campuses
How to Choose an Intrusion Detection Security Camera System for Corporate Campuses
Tools and Platforms Worth Evaluating
You have four broad options, each with a trade-off profile.
Option categories
First, cloud APIs from big vendors: Amazon Rekognition and Microsoft Azure Face API. They scale, document well, and support both 1:1 and 1: N. However, you still need to handle video ingest, watchlist logic, and alert routing. Pricing by request and match count can surprise you at scale.
Second, open-source toolkits like InsightFace. They are fast and strong in benchmarks. With engineering time, you can tailor thresholds and storage. On the other hand, you must own reliability, security hardening, and legal audits. That is fine for R&D labs; it is tough for small teams with no ML stack.
Third, AI video intelligence platforms that bundle face recognition with other engines. Tools like VideoraIQ combine face recognition with intrusion, fire/smoke, ANPR, and unattended object detection. The platform integrates with existing IP-based CCTV systems without additional hardware, and it’s cloud-based with no need for on-premise servers. In 2026, that can trim rollout time across many sites.
"We went from finding out about incidents in the morning briefing to being notified in real time. VideoraIQ caught an intruder at 2AM that our overnight guard missed. That one event alone justified the entire platform cost." — Ananya Mehta, Head of Facilities
Maturity signals
Moreover, look for social proof to gauge maturity. For example, VideoraIQ states 10,000+ cameras monitored and deployments in 7+ countries. That doesn’t pick the winner for you, but it hints at scale and support depth.
Finally, match tools to your constraints. If you need strict data residency, check region availability and lawful bases. If you need alerts in under three seconds, ask to measure on your stream. If you need to manage many sensor types, a bundle with 9 detection engines can cut tool sprawl.
**Schedule a free pilot review →
What to Do After You Pick a System
Your work starts after the contract. A clean rollout prevents false alerts and privacy headaches.
-
Enroll well. Capture at least three images per person: front, slight left, slight right, with and without glasses if allowed. Use consistent lighting. Tag each entry with a lawful basis and consent record where required. Set a review task for stale enrollments.
-
Set confidence thresholds by zone. A staff-only lab may need a higher bar than a lobby. Start stricter for 1: N searches to reduce false hits, then lower if you miss urgent matches. Document who can change thresholds and when.
-
Train your team on alerts. Show examples of Real-time alerts with video proof, location tag, and timestamp so people know what “good” looks like. Define actions for “match,” “possible match,” and “no match.” Measure response times and coach to target.
-
Create a data retention policy. Decide what to store (faceprints, thumbnails, alert clips), where, and for how long. Shorter is safer. Tie deletion to case status and legal holds.
-
Schedule quarterly accuracy audits. Sample alerts by zone and time of day. Track false accepts/rejects, and adjust thresholds. Review fairness metrics by demographic group. Share results with legal and leadership.
- Enrollment checklist:
- 3–5 images per person, varied angles
- Consent recorded and traceable
- Clear zone-based thresholds
- Alert playbooks in writing
- Quarterly audit calendar set
As you refine, keep your original goal in sight. You chose this system to cut risk and speed response. Make sure your dashboard and reports show those gains.
Therefore, if your team needs to choose facial recognition system settings again for a new site, reuse this rollout kit and tune only what changes.
Key Takeaways
- Start with the job, not the demo. Define 1:1 vs 1: N, hard scenes, and the cost of error.
- Use independent tests. Check NIST FRVT once, then prove it on your cameras in a 30‑day pilot.
- Demand fairness and privacy. Keep per‑group metrics, GDPR/HIPAA alignment, and deletion rules.
- Measure speed and scale. Target <3 seconds alert latency and clean links to your VMS or SIEM.
- Bundle with care. Platforms with 9 detection engines can reduce tool sprawl and training time.
What to Do This Week
Block two hours with security, legal, and IT to draft your one-page test plan. Pick one busy entrance and one “hard” zone for the pilot. Pull NIST FRVT results for three vendors, line up sample enrollments, and request a live test by Friday. Then track alerts, false matches, and response times for one week.
**Get an instant expert consult →
Finally, keep your notes. In 2026 and beyond, your audit trail, and the way you chose, will matter as much as the system you picked.

